
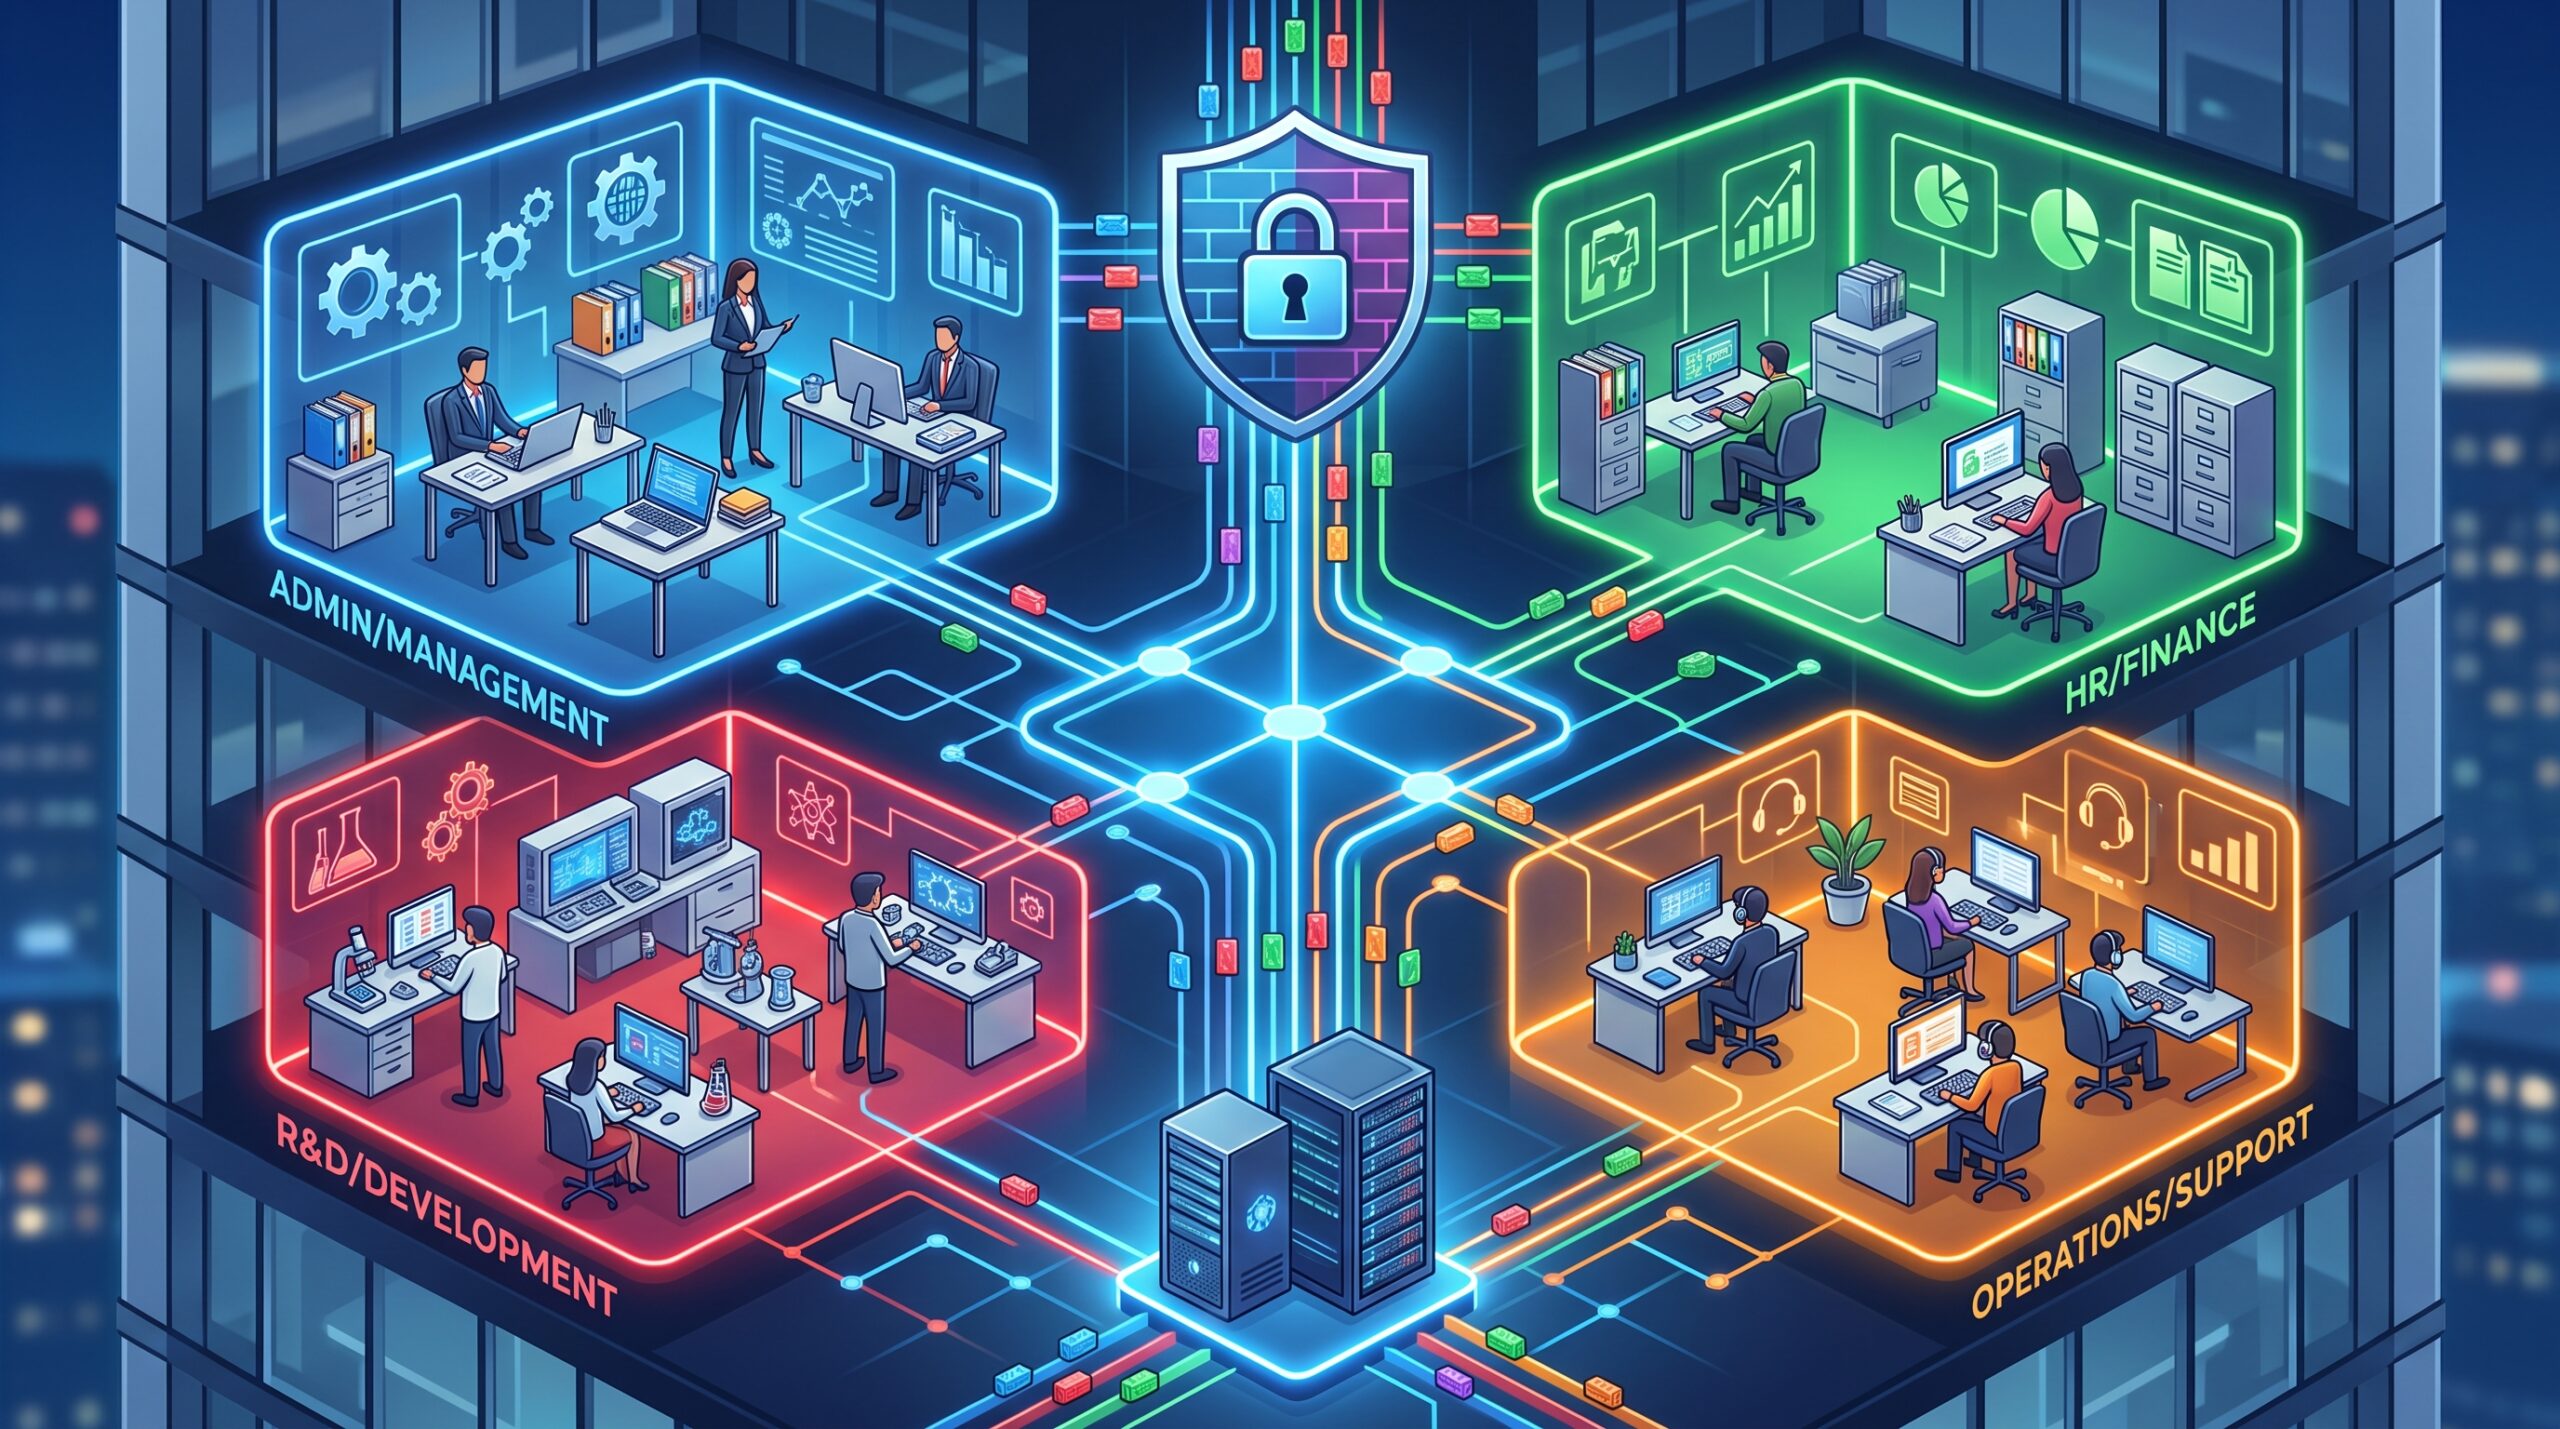
Network segmentation separates groups of devices and controls how they communicate. VLANs provide logical separation; firewall or access-control policies enforce the permitted connections between those groups.
What a VLAN changes
VLANs organise traffic into logical segments on shared infrastructure. Typical segments include voice, guest access, staff devices and management.
Control traffic between segments
Inter-VLAN firewall policies are essential. Merely creating VLAN IDs does not stop permitted routes or compromised accounts from crossing boundaries.
Practical decision guidance
Document required traffic before blocking it. A staff computer may need a printer, while a CCTV recorder may need cameras but no access to payroll files. Restrict management interfaces to authorised administrators and maintain a record of rule changes. Overly broad permissions can undo the value of segmentation.
Applying this to your business
Illustrative design: guest Wi-Fi reaches the internet, staff devices reach approved business services, and camera traffic stays in its own segment. Test both allowed and prohibited connections after changes. Keep a controlled rollback option for essential services that behave unexpectedly.
Before you proceed
- Inventory devices and application dependencies.
- Define permitted traffic between groups.
- Test isolation with real client devices.
Ask ITC Systems to review your network access design. Call 031 001 7028 or email [email protected].
Related service: https://itcsystems.co.za/network-infrastructure/
Related guide when published: https://itcsystems.co.za/blog/slow-office-wifi-durban/