
Home > Case Studies > Cybersecurity
CASE STUDY · Cybersecurity
Cybersecurity Case Study for an Umhlanga Business
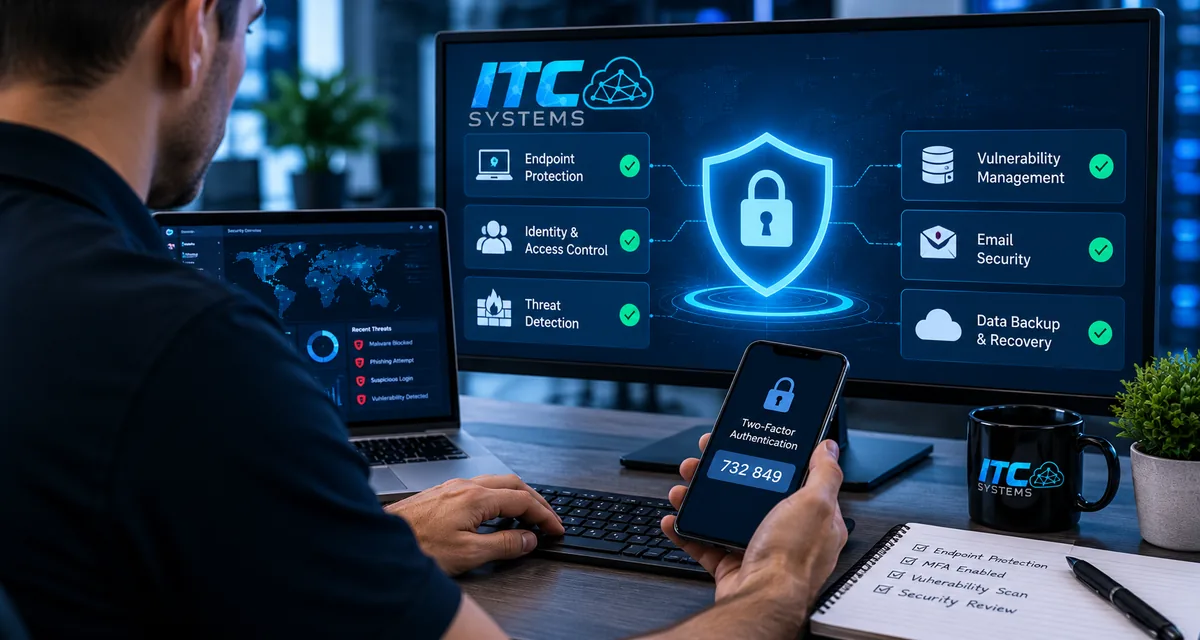
ITC Systems introduced layered cybersecurity controls for a professional services organisation in Umhlanga, Durban. The work addressed gaps in endpoint protection, account security, patching and firewall management. Managed endpoint detection and response, multi-factor authentication and vulnerability reviews brought these controls into a more coordinated approach to ongoing security management.
The Challenge
An assessment identified inconsistent endpoint protection, gaps in multi-factor authentication adoption and weaknesses in patching, firewall policies and vulnerability management.
The ITC Systems Solution
ITC Systems implemented endpoint detection and response, strengthened account protection with multi-factor authentication, and managed firewall policies and security patching. Vulnerability scanning and ongoing reviews provided a process for identifying, prioritising and tracking remediation work.
Project Outcome
The organisation gained more centralised visibility across endpoints, accounts and network security. The project established an ongoing vulnerability-management process rather than treating the initial assessment as a once-off exercise.
Technical Scope Implemented
Managed Endpoint Detection & Response (EDR)
Mandatory Multi-Factor Authentication (MFA)
Automated Vulnerability Scanning & Patching
Strict Next-Gen Firewall Access Control
Protect your enterprise data against ransomware & phishing
Discover how our layered cybersecurity model keeps South African businesses resilient and POPIA compliant.
Frequently asked questions
Plan your next step
Unsure where your business is exposed? Ask ITC Systems to assess your cybersecurity controls and prioritise improvements for your Durban or KZN organisation.